What Is OWASP Top 10?
June 10, 2026
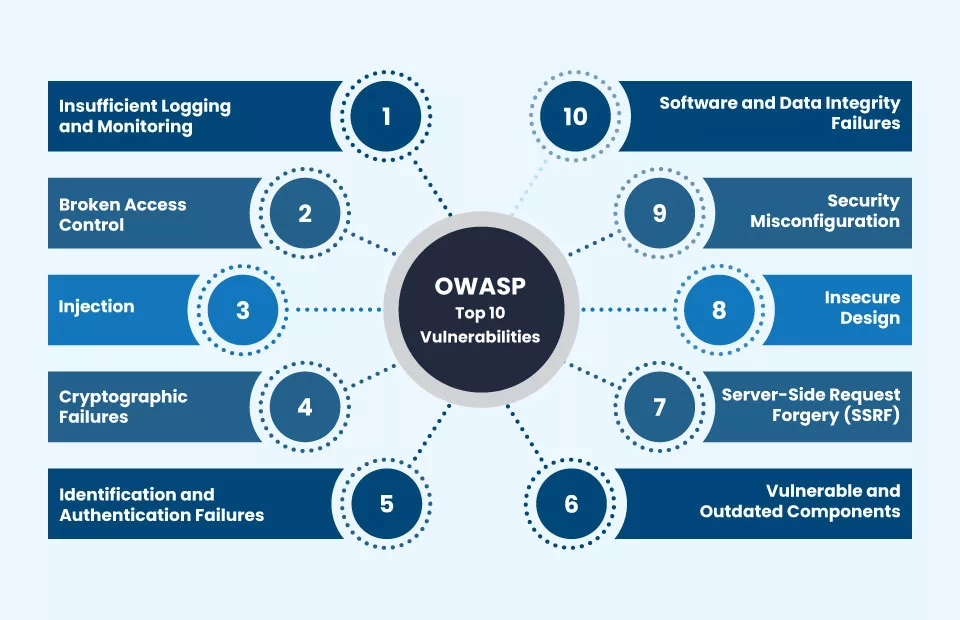
OWASP Top 10 is a standard awareness document published by the Open Web Application Security Project (OWASP), listing the ten most critical security risks to web applications. It serves as a foundational reference for developers, security professionals, and organizations aiming to build more secure software.
The list is compiled based on data from security researchers and organizations worldwide, ranking vulnerabilities by their prevalence, exploitability, and potential impact. Common entries include Broken Access Control, Cryptographic Failures, Injection (such as SQL Injection), and Security Misconfiguration.
Understanding OWASP Top 10 is essential not only for penetration testers, but also for software engineers, since many of these vulnerabilities originate from insecure coding practices during development. By learning this list, developers can proactively prevent security flaws instead of fixing them after deployment.
Practicing these concepts hands-on, for example through platforms like TryHackMe, helps bridge the gap between theory and real-world exploitation scenarios, giving a clearer picture of how attackers think and how to defend against them.
As web applications grow more complex, OWASP regularly updates this list to reflect emerging threats, making it a living reference that every developer and security enthusiast should keep revisiting.